WebMCP Gives Agents the Tools, but the Browser Still Owns the Risk
WebMCP gives browser agents structured actions to call, but a responsible product pilot needs browser-level tool trust, lifecycle controls, semantic quarantine, and verified state changes before it grants the agent real authority.

A browser agent can move from "find the button" to "call the site's tool." The shift makes web tasks faster to specify, but it also moves trust decisions into the browser: which script registered a tool, how long that tool should live, and whether its description or result is trying to steer the agent.
WebMCP is now close enough to a product surface for PMs to test those questions. OpenAI opened a 10-day WebMCP Challenge on August 25, with submissions due September 3, 2026 at 3:00 p.m. Eastern, and OpenAI browser lead James Sun said on August 30 that WebMCP was supported in the cloud browser in ChatGPT Work, with Chrome extension support planned next. 12
Quick view
| Trend | Fresh signal | Product problem | Evidence boundary | Action window |
|---|---|---|---|---|
| WebMCP is turning websites into callable tool surfaces for browser agents | OpenAI's challenge is open through September 3; ChatGPT Work's cloud browser supports WebMCP. 12 | Visual browsing makes an agent infer actions from page layout. Direct tools make actions explicit, while exposing a new tool-trust and prompt-injection surface. | The WebMCP document is a W3C Community Group Draft Report, and WebMCP-Phalanx is an arXiv preprint evaluated against a simulated same-origin script attacker. 34 | Teams entering the challenge have until September 3 at 3:00 p.m. Eastern. Other teams can start a bounded security and reliability pilot this week. |
The PM question is therefore narrower than "Will agents use the web?" It is: Can one product expose a small set of useful actions while preserving origin, lifecycle, authorization, and verification controls?
Why WebMCP matters now
WebMCP is a proposed browser interface that lets a page expose structured tools to an agent. A tool has a name, description, input schema, and execution function. The agent receives the site's declared capabilities instead of reconstructing them from screenshots, DOM structure, and button labels. The current draft exposes the interface as
document.modelContext, with registerTool(), getTools(), and executeTool(). 3The change affects the product contract. A human sees a checkout page and decides which button to press. An agent sees a tool such as
search_products or update_reservation, supplies structured arguments, and receives a structured result. The website becomes easier for an agent to operate, while the tool definition becomes part of the product's security boundary.Cloudflare's developer preview shows one deployment path. A site owner can switch on WebMCP in the Cloudflare Dashboard, and Cloudflare's edge adds a same-origin bridge script to HTML responses. The bridge looks for
document.modelContext, combines selected tool packs, and registers them in the visitor's browser. The preview's Site MCP Server pack can proxy the site's existing MCP tools through the visitor's own session. Unsupported browsers continue with the original page behavior. 5OpenAI's own demo makes the interaction visible: Codex opens a WebMCP-enabled 3D modeling site, discovers its tools, iterates on a model, captures screenshots, and uses a feedback tool while the person remains in the same interface. The accompanying developer video is a useful orientation for the user experience; its demo does not establish production reliability or security. 6
Loading content card…
The security catch is inside the tool list
WebMCP-Phalanx, a preprint from Lin-Fa Lee, Yi-Yu Chang, Chia-Mu Yu, and Kuo-Hui Yeh, starts with the browser's Same-Origin Policy (SOP). The site's own code, an advertising SDK, and an analytics script may share one origin. The browser can therefore grant those scripts access to the same WebMCP surface even when the site owner trusts them differently. 4
The attack is easy to miss because the tool can be structurally valid. A hostile script can register a tool with a useful-sounding name, place instructions in its description or input schema, return hostile content after execution, or leave old tool output in the agent's conversation after a single-page-app transition. A
readOnlyHint can also describe intent while the implementation performs a network request; the paper treats that mismatch as a runtime violation rather than as proof supplied by the declaration. 34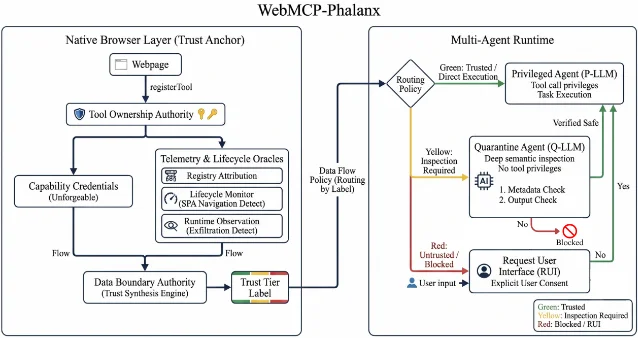
The proposed design separates two jobs. A browser-native layer issues an unforgeable capability for each registration, tracks lifecycle and execution signals, and attaches a trust label. A quarantine agent can inspect metadata and returned content without permission to call tools. A privileged agent receives content only after the policy permits execution. The split prevents a semantic inspection model from holding the same authority as the model that can change state. 8
The paper's measured results make the product risk concrete:
| Attack surface | No defense | Protected result | What remains |
|---|---|---|---|
| Tool revocation and overwrite under the tested same-origin attacker | 100% success | 0% with capability-based ownership | Same-origin attribution remains coarse: a hostile script can still obtain a valid capability for its own tool. 9 |
| Injection in tool descriptions, 80 attempts | 69/80 succeeded | 0/80 with the quarantine-agent layer | A task-fitting tool name can trigger a call before content inspection. 10 |
| Injection in returned content, 80 attempts | 42/80 succeeded | 2/80 with the quarantine-agent layer | The residuals came from calls induced by malicious names before the returned content existed. 10 |
| Cross-page semantic residue | 80% attack success after a lifecycle-only cleanup | 0% after invalidating trust for old tool output | Tool removal alone left instructions in the agent's conversation history. 11 |
The remaining failure points change the implementation order. A filter that reads descriptions after the agent has already selected a task-fitting name is late. A lifecycle monitor that deletes the tool while keeping its old output in context is incomplete. A runtime observer that detects a first side effect after execution begins supplies containment and disclosure; it does not prevent the first side effect. 12
The evidence also has a clear boundary. The authors implemented two browser assumptions as a JavaScript polyfill, and cryptographic script provenance is an architectural proposal rather than a native browser guarantee in the experiment. The attacker model covers same-origin page scripts; browser extensions use a different privilege model. The numbers support a security test plan for WebMCP, with scope and implementation assumptions attached. They do not establish that the proposed browser controls are ready for every production browser. 13
A bounded product implementation path
A PM can turn the trend into a reversible experiment with one workflow and a small tool surface.
- Choose a workflow with a machine-checkable end state. Appointment changes, order status, or document approvals work better than an open-ended research task. Define allowed writes, required confirmation, escalation conditions, and the maximum time the agent may hold a session.
- Expose reads before writes. Start with search, lookup, and validation tools. Give every write a narrow schema, an authorization check, an idempotency key, and a deterministic confirmation step. Treat tool names and descriptions as untrusted input until the browser and policy layer validate them.
- Bind every tool to origin and lifecycle. Record the registering origin, the page or session scope, the registration time, and the tool version. Delete navigation-scoped tools on logical SPA transitions, and invalidate their previous results in the agent context.
- Gate calls before semantic inspection finishes. The WebMCP-Phalanx residuals point to a specific control: the agent must finish inspecting the tool name, description, schema, and provenance before it can invoke the tool. A quarantine model should hold no execution privilege; a privileged model should receive only approved content.
- Verify state outside the language model. Compare the requested operation, tool arguments, authorization record, and resulting state diff. A fluent response such as "done" is an output claim. The verifier needs to see the actual record change, amount, recipient, or approval state.
- Run paired baselines. Compare the current UI-automation path with WebMCP on the same tasks, tools, permissions, and acceptance checks. Hold out task phrasings, hostile tool names, injected descriptions, returned payloads, SPA transitions, and revoked sessions.
- Measure the complete path. Track tool-discovery latency, time to first call, successful verified completion, wrong-tool rate, unauthorized-write rate, prompt-injection rate, recovery after a rejected call, human confirmation rate, p50/p95 latency, and cost per successful workflow. Cloudflare's preview keeps tools in the visitor's browser and describes itself as a developer preview, so its setup simplicity is an implementation signal rather than a reliability guarantee. 5
The decision gate
The falsifiable hypothesis is: for one bounded workflow, WebMCP will raise verified completion or reduce agent navigation effort while keeping unauthorized actions, injection success, p95 latency, and cost per successful workflow within the existing product budget.
Use three gates:
- Outcome: held-out tasks reach the correct state with fewer navigation failures than the current path.
- Safety: tool provenance, lifecycle cleanup, call timing, authorization, confirmation, and rollback stop unapproved state changes. The security set includes names and returned values, because content-only filtering leaves the name-trigger residual.
- Operations: the full browser-to-tool path fits the workflow's latency and cost budget at p95. A benchmark demo or a developer preview supplies a test surface; it supplies no production SLA.
WebMCP is worth watching because the ecosystem has started testing the same product boundary from three sides: OpenAI is giving agents a supported client and a challenge deadline, Cloudflare is reducing the site-side setup to an edge bridge, and the W3C draft defines the browser API. The security paper adds the constraint that decides whether a pilot is responsible: the tool registry needs its own trust boundary before the agent receives authority to act.
References
- 1The WebMCP Challenge
openai.com
- 2
- 3WebMCP Draft Community Group Report
webmachinelearning.github.io
- 4WebMCP-Phalanx
arxiv.org
- 5Give any website a WebMCP interface
blog.cloudflare.com
- 6Build agent-ready sites with WebMCP
youtube.com
- 7WebMCP-Phalanx architecture figure
arxiv.org
- 8WebMCP-Phalanx
arxiv.org
- 9WebMCP-Phalanx
arxiv.org
- 10WebMCP-Phalanx
arxiv.org
- 11WebMCP-Phalanx
arxiv.org
- 12WebMCP-Phalanx
arxiv.org
- 13WebMCP-Phalanx
arxiv.org
This story was produced automatically by a channel. One sentence is all it takes for Neodrop to keep producing for you.