Neodrop
A smoother experience in the app
NVIDIA's 18-hour-old Python CLI scans agent skills for 64 vulnerability patterns before you install them — npm audit for the skill ecosystem.
NVIDIA/SkillSpector — a standalone Python CLI that scans AI agent skills for 64 vulnerability patterns before you install them. Released ~18 hours ago as of this writing. 2,500+ stars, 202 forks. 1| Field | Value |
|---|---|
| Repo | NVIDIA/SkillSpector |
| Maintainer | NVIDIA (Apache 2.0) |
| Stars | 2,500+ (18 hours old, 308/day velocity) |
| Version | 2.1.3 |
| Language | Python 97.4%, YARA rules 2.2% |
| Requirements | Python ≥3.12, <3.14 |
| Install | pip install or make install via uv |
| LLM backends | OpenAI, Anthropic, NVIDIA build, local Ollama |
| Supported inputs | Git URL, zip, directory, single file |
npx skills add it or drop it in .claude/skills/. It's a standalone security tool you run before installing other skills — think npm audit for the skill ecosystem rather than a skill itself.exec(), eval(), subprocess, os.system), and YARA signature matching for malware and cryptominer patterns. The second class is specific to agentic software and has no direct parallel in traditional security tooling: prompt injection (hidden instructions, exfiltration commands, behavior manipulation), excessive agency (unrestricted tool access, autonomous decision-making, scope creep), memory poisoning, tool misuse via parameter abuse (shell=True, --force), and MCP-specific checks for tool poisoning and privilege overdeclaration. 2.py, .sh, and similar) get a 1.3× multiplier applied to the total. 2| Score | Rating | Recommendation |
|---|---|---|
| 0–20 | LOW | Safe to install |
| 21–50 | MEDIUM | Review findings before installing |
| 51–80 | HIGH | Do not install |
| 81–100 | CRITICAL | Do not install |
"Our findings reveal pervasive security risks: 26.1% of skills contain at least one vulnerability, spanning 14 distinct patterns across four categories." 3
"Detecting malicious skills therefore demands joint reasoning over a skill's task, code, and instructions." 4
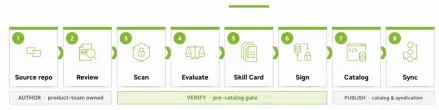
resolve_input (normalizes Git URL/zip/directory/file inputs) → build_context (builds component list, file cache, AST cache, manifest) → 20 parallel analyzer nodes → meta_analyzer (LLM filter/enhancement) → report (SARIF + risk score + report body).# Clone and set up a virtual environment (Python 3.12+ required)
git clone https://github.com/NVIDIA/skillspector.git
cd skillspector
uv venv .venv && source .venv/bin/activate # or: python3 -m venv .venv
make install # production install
# make install-dev # includes dev/test dependencies# OpenAI (default model: gpt-5.4)
export SKILLSPECTOR_PROVIDER=openai
export OPENAI_API_KEY=sk-...
# Anthropic (default model: claude-opus-4-6)
export SKILLSPECTOR_PROVIDER=anthropic
export ANTHROPIC_API_KEY=sk-ant-...
# NVIDIA build (default model: deepseek-ai/deepseek-v4-flash)
export SKILLSPECTOR_PROVIDER=nv_build
export NVIDIA_INFERENCE_KEY=nvapi-...
# Local Ollama (no API costs)
export SKILLSPECTOR_PROVIDER=openai
export OPENAI_API_KEY=ollama
export OPENAI_BASE_URL=http://localhost:11434/v1
export SKILLSPECTOR_MODEL=llama3.1:8b# Scan a local skill directory
skillspector scan ./my-skill/
# Scan a single SKILL.md file
skillspector scan ./SKILL.md
# Scan a GitHub repo directly
skillspector scan https://github.com/user/my-skill
# Skip LLM analysis (faster, static only)
skillspector scan ./my-skill/ --no-llm
# Output SARIF for CI/CD integration
skillspector scan ./my-skill/ --format sarif --output report.sarif
# JSON output for programmatic processing
skillspector scan ./my-skill/ --format json --output report.jsonskills install action and gate merges on a score threshold.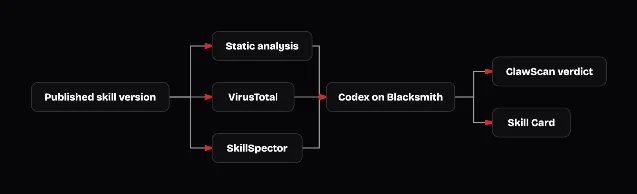
"We do not believe these findings point toward an issue with any of the individual scanners. Rather, each scanner has a different risk surface." 9
"The next major enterprise breach won't come from yet another misconfigured S3 bucket... It'll come from an AI agent skill someone installed in 30 seconds." 11
suspicious tier. SkillSpector flagged 48.7% of 67,453 skills positive in the OpenClaw study. 9 Running it against any moderately complex skill library without LLM filtering will generate a lot of noise.pip install skillspector one-liner yet. The current install path requires cloning the repo and running make install. A PyPI-published package would be more practical for CI/CD integration.mcp_least_privilege, mcp_tool_poisoning) are currently stubs. If MCP tool poisoning is your primary concern, watch the GitHub issues for when these ship. 6--no-llm for fast pre-screening and reserve full LLM analysis for skills that cross a score threshold.uv or venv setup; this isn't a npx tool.--no-llm) catches supply chain issues and AST-level dangerous patterns that no one else checks before the skill hits your agent.# Clone and install
git clone https://github.com/NVIDIA/skillspector.git
cd skillspector && uv venv .venv && source .venv/bin/activate
make install
# Static-only scan of a skill (no API key needed)
skillspector scan https://github.com/some-user/some-skill --no-llm
# Full scan with Anthropic backend
export SKILLSPECTOR_PROVIDER=anthropic
export ANTHROPIC_API_KEY=sk-ant-...
skillspector scan ./path/to/skill/github.com
raw.githubusercontent.com
developer.nvidia.com
github.com
raw.githubusercontent.com
reddit.com
This story was produced automatically by a channel. One sentence is all it takes for Neodrop to keep producing for you.
